Manual, senior-led testing for teams that need more than a scan report
We test the way an attacker would: mapping your application’s logic, chaining findings, and proving what an adversary could actually reach. Then we stay with your team until the findings are closed.
Supports SOC 2, ISO 27001, PCI DSS and HIPAA requirements. QSA-led where PCI DSS applies.
Senior testers only.
No junior handoffs, no template reports, no findings you have to translate before your engineers can act on them.
Our penetration testing spans your full attack surface — applications, APIs, mobile, networks, cloud, infrastructure, and business logic. Whether driven by compliance, client demands, product changes, or proactive security goals, we tailor each engagement to your trigger and timeline. The outcome is always the same: clear risk visibility and actionable remediation.
Web Application Penetration Testing
Identify injection flaws, authentication weaknesses, misconfigurations, business logic issues, and critical vulnerabilities across modern web applications.
Assess AI systems and machine learning models for adversarial attacks, prompt injection, data poisoning, model manipulation, and security control weaknesses.
Uncover misconfigurations, privilege escalation paths, exposed services, insecure IAM policies, and security gaps across AWS, Azure, and GCP environments.
Detect broken access controls, authentication bypass, excessive data exposure, rate-limit issues, and injection vulnerabilities in REST and GraphQL APIs.
Expose security flaws in iOS and Android applications, including insecure storage, authentication weaknesses, encryption issues, and backend API risks.
Our penetration testing consulting helps your team define scope, choose the right testing approach, understand risk, prioritize remediation, and prepare for client, audit, or compliance requirements. GRSee works closely with your technical and leadership teams before, during, and after testing.
Deep business logic testing that goes beyond automated scans to uncover the vulnerabilities that actually matter to your business.
Senior experts involved throughout the entire engagement, from scoping to final review. No junior handoffs, no surprises.
Clear, risk prioritized findings with actionable remediation guidance so your team knows exactly what to fix and in what order.
White glove partnership until resolution, not just a report drop. We stay with you until every finding is addressed.
Structured, transparent engagement with clear timelines, regular communication, and full visibility into the process.
Do you need a manual pentest, or will an automated one do?
Worth asking honestly, because the automated tools have got better and sometimes the answer is that you don’t need us yet.
Here’s the pattern we see from teams who run one before coming to us. It’s fast, often a day or two. The report is usually clean enough to put in front of an auditor. It surfaces a healthy volume of findings, weighted heavily toward medium and low severity, with a few false positives to sort through. Teams are generally happier with it than they expected to be.
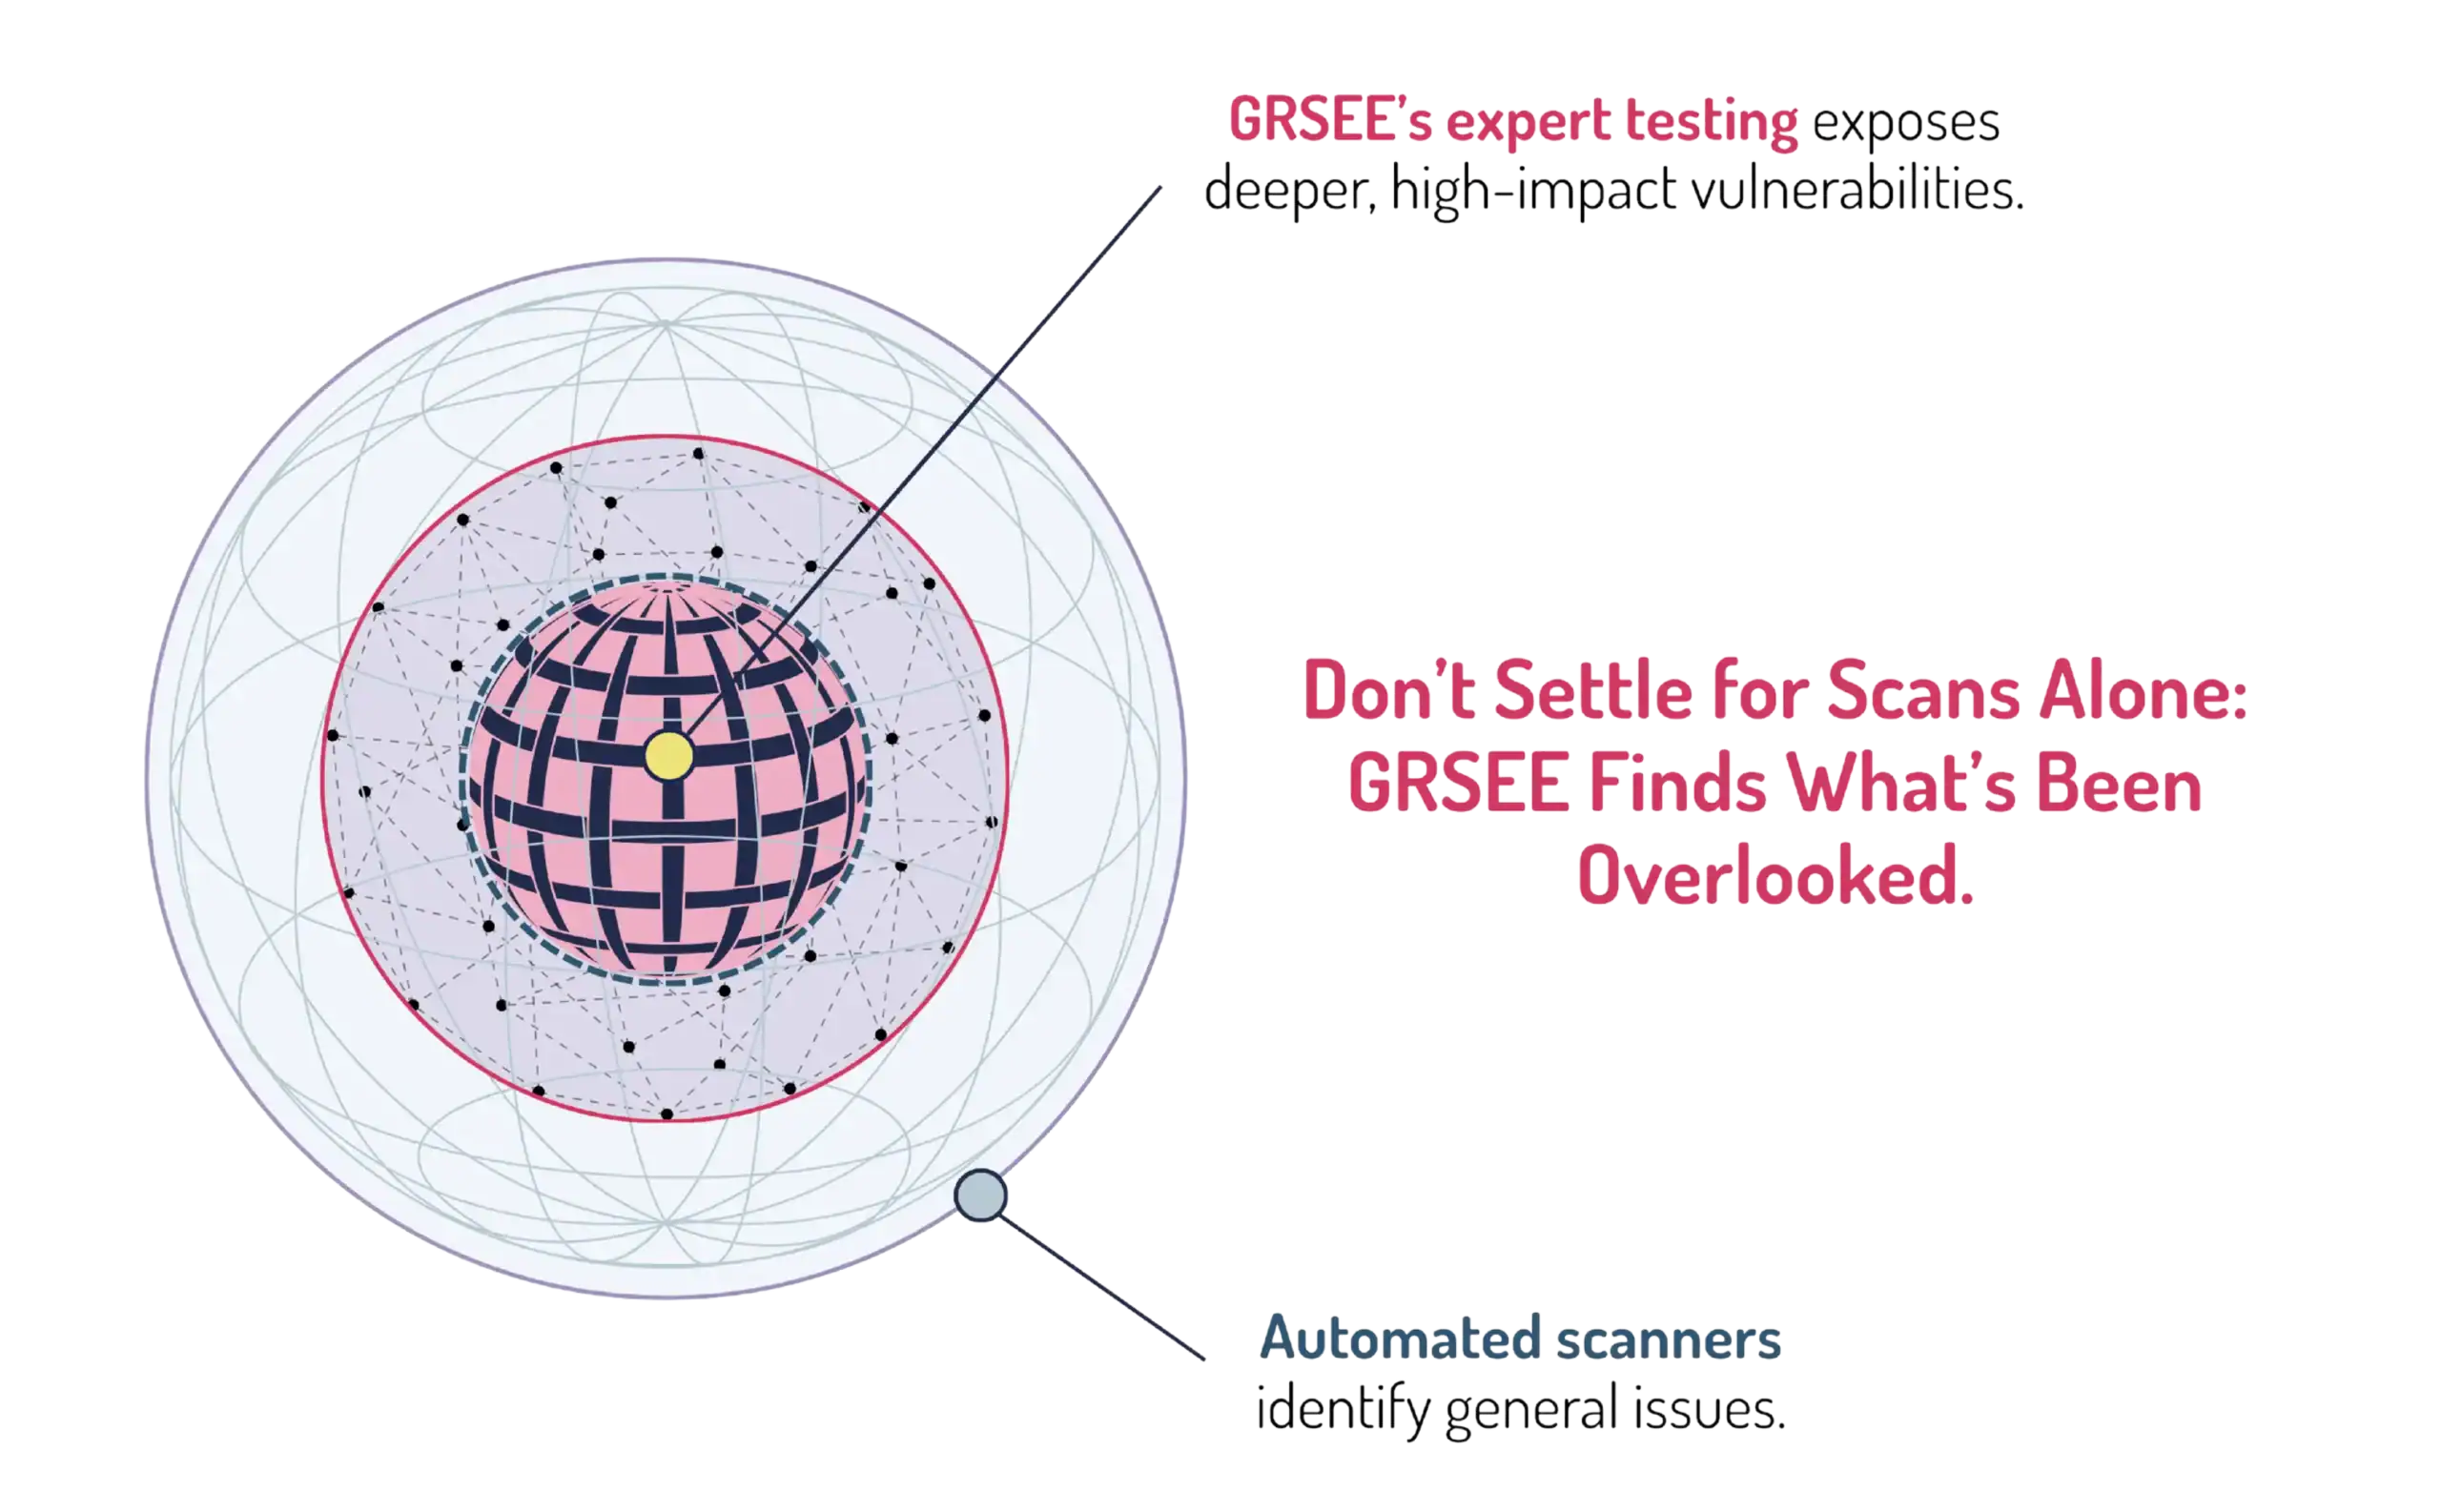
Then the caveats show up. The severity distribution is the tell: automated testing finds what it has a signature for. Known vulnerability classes, misconfigurations, injection points, outdated components, exposed headers. Real breadth, genuinely useful, and almost none of it in the category that shows up in incident post-mortems.
What automation can’t do is reason about your business. It doesn’t know that your refund endpoint should be unreachable once an order settles, or that a tenant ID sitting in a URL parameter means one customer can read another’s data, or that chaining three low-severity findings gets an attacker to your admin panel. Those require someone who understands what your application is for and where its assumptions live. That’s the judgment gap, and no amount of request volume closes it.
An automated test is probably enough if
You have a small codebase and a straightforward permission model
You need evidence for a specific framework or client questionnaire on a deadline
You've never been tested and want a baseline before investing in depth
Your auditor has confirmed in writing what they'll accept
You need a manual test if
Your application has multi-tenancy, role hierarchies, approval workflows, or money movement
You're in scope for PCI DSS, where the testing methodology itself is assessed
An enterprise customer or their security team will read the report
You've already had automated testing and want to know what it missed
A breach in your application would end the business rather than interrupt it
On "audit-viable"
Automated reports do get accepted. We’ve seen it. Whether yours will depends on the framework, the auditor, and how your own risk assessment classifies the application.
PCI DSS Requirement 11.4 sets expectations around methodology and tester independence that a scan-driven report generally won’t meet.
SOC 2 and ISO 27001 leave auditors more latitude, and they use it differently.
Ask your auditor before you buy rather than after. Or ask us, we’ll tell you if you don’t need us, and we do say that fairly often.
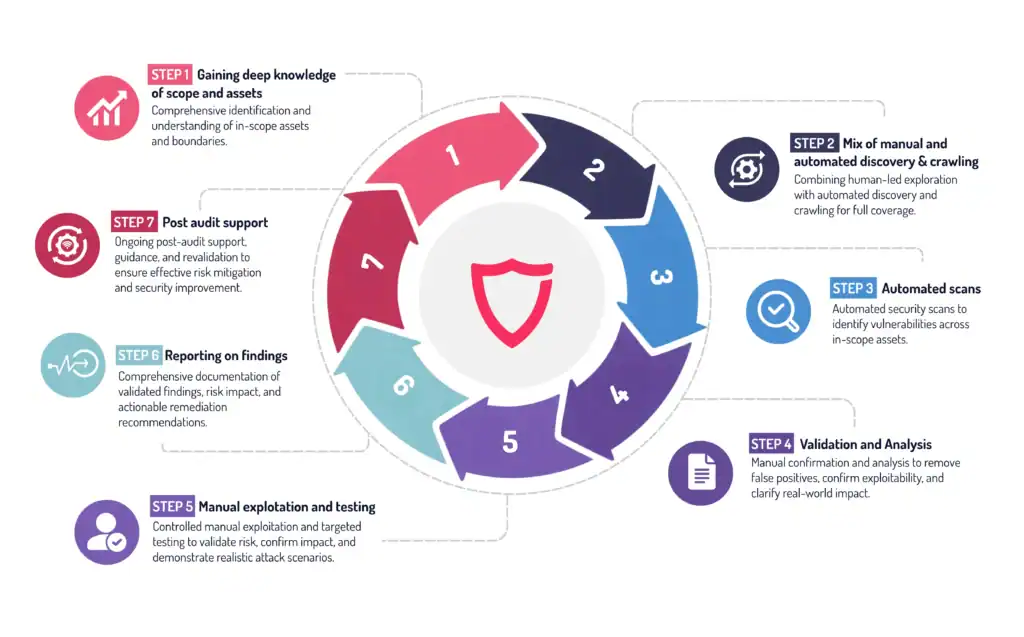
Penetration testing is a controlled security assessment where ethical hackers simulate real-world attacks against your systems, applications, or infrastructure to uncover vulnerabilities before attackers do.
Unlike automated scans alone, penetration testing goes deeper. It validates whether weaknesses are actually exploitable and shows you the real business risk behind them.
How is a penetration test different from a vulnerability scan?
A vulnerability scan is automated and designed to identify known issues at a high level. A penetration test combines automation with manual testing by experienced security professionals who actively investigate, validate, and attempt to exploit weaknesses.
In simple terms: a scan tells you what might be wrong. A penetration test shows you what could actually be used against you.
What types of penetration testing does GRSee offer?
GRSee supports several types of penetration testing, including:
Web application penetration testing
API penetration testing
Mobile application penetration testing
Network penetration testing
Cloud penetration testing
AI penetration testing
Red team engagements
Each engagement is tailored to the environment and business risk, rather than using a one-size-fits-all checklist.
Will testing disrupt our operations?
A well-run penetration test should be carefully planned to minimize disruption.
We coordinate with your team in advance, define rules of engagement, and use controlled testing methods. If needed, testing can often be performed in staging or lower environments instead of production.
What do you need from us before testing starts?
For a smooth engagement, we typically need:
Clear scope of what should be tested
A point of contact from your team
Access details, if authenticated testing is included
Testing windows or operational constraints
Any specific business concerns or high-risk areas you want us to focus on
We guide this process closely so your team is never left guessing. That’s part of our white-glove approach.
How long does a penetration test take?
Most penetration tests take 2 to 6 weeks, depending on the number of assets, scope, and complexity of the environment. Simpler tests may move faster, while more complex environments or multi-surface assessments take longer.
Do you retest after we fix the findings?
Yes. We provide retesting to verify that vulnerabilities have been properly remediated and that fixes are effective before findings are closed.
Can a penetration test support our compliance requirements?
Yes. Penetration testing often supports frameworks and client requirements such as PCI DSS, SOC 2, ISO 27001, HIPAA, and others.
It can also strengthen audit readiness by validating that controls are working in practice, not just on paper.
Do you provide remediation guidance after the penetration test?
Yes. Every engagement includes detailed remediation guidance to help your team understand the root cause, business impact, and recommended fixes for each finding. We also work closely with your internal teams to clarify technical issues and support remediation efforts where needed.
Can we use an automated or AI-driven pentest instead?
Sometimes, yes. If you have a small codebase, a simple permission model and a deadline, an automated test may give you what you need. It won’t reason about your business logic, and the finding mix tends to skew medium and low as a result. We’ll tell you honestly which side of that line you’re on.
Will our auditor accept the report?
For SOC 2, ISO 27001 and HIPAA, our reports are built to be used as evidence and we’ve never had one rejected. For PCI DSS, the methodology and tester independence are themselves in scope, and we test accordingly. If your auditor has specific requirements, send them to us before we scope.
Who actually does the testing?
Named senior testers, assigned before you sign, with their certifications listed in the proposal. You’ll meet them on the kickoff call and they’re the same people on the debrief. [Add the actual cert mix — OSCP, OSWE, CREST, whatever is accurate.]
What does a penetration test cost?
Pricing is driven by scope: number of applications, user roles, API surface, and whether testing is authenticated. A single web application with a standard role model typically falls in [range]. We scope on a 30-minute call and quote a fixed price, so there are no change orders mid-test.
Contact GRSee today to schedule a call and discuss your security testing needs.